Insights
An 11-minute agent exploit makes response speed a security control
Amazon says Cairn agents reached arbitrary file write in a medical-imaging app in about 11 minutes. The incident makes containment time part of the threat model, while long failed campaigns show that persistence matters as much as capability.
· 2 min read

Latest in each category
Browse all insights
XYBench shows agent evaluations must test the problem behind the request
Ai2 found that five models often answered a user's proposed method while missing the underlying goal. Agent teams should test whether a system can redirect a mistaken request before it acts.
· 2 min read
ISO 42005 turns AI impact assessment into evidence, not a risk-register checkbox
AWS's mapping to ISO/IEC 42005 shows the practical shift: AI impact assessment must connect intended use, affected parties, measured impacts and treatment decisions. Governance teams need an evidence trail, not another static register.
· 2 min read
Microsoft's agent backdoors make checkpoint provenance an execution control
Two post-training attacks produced unsafe tool calls across coding-agent environments. Teams need to verify data and model origins, then constrain what an adopted model can execute.
· 2 min read
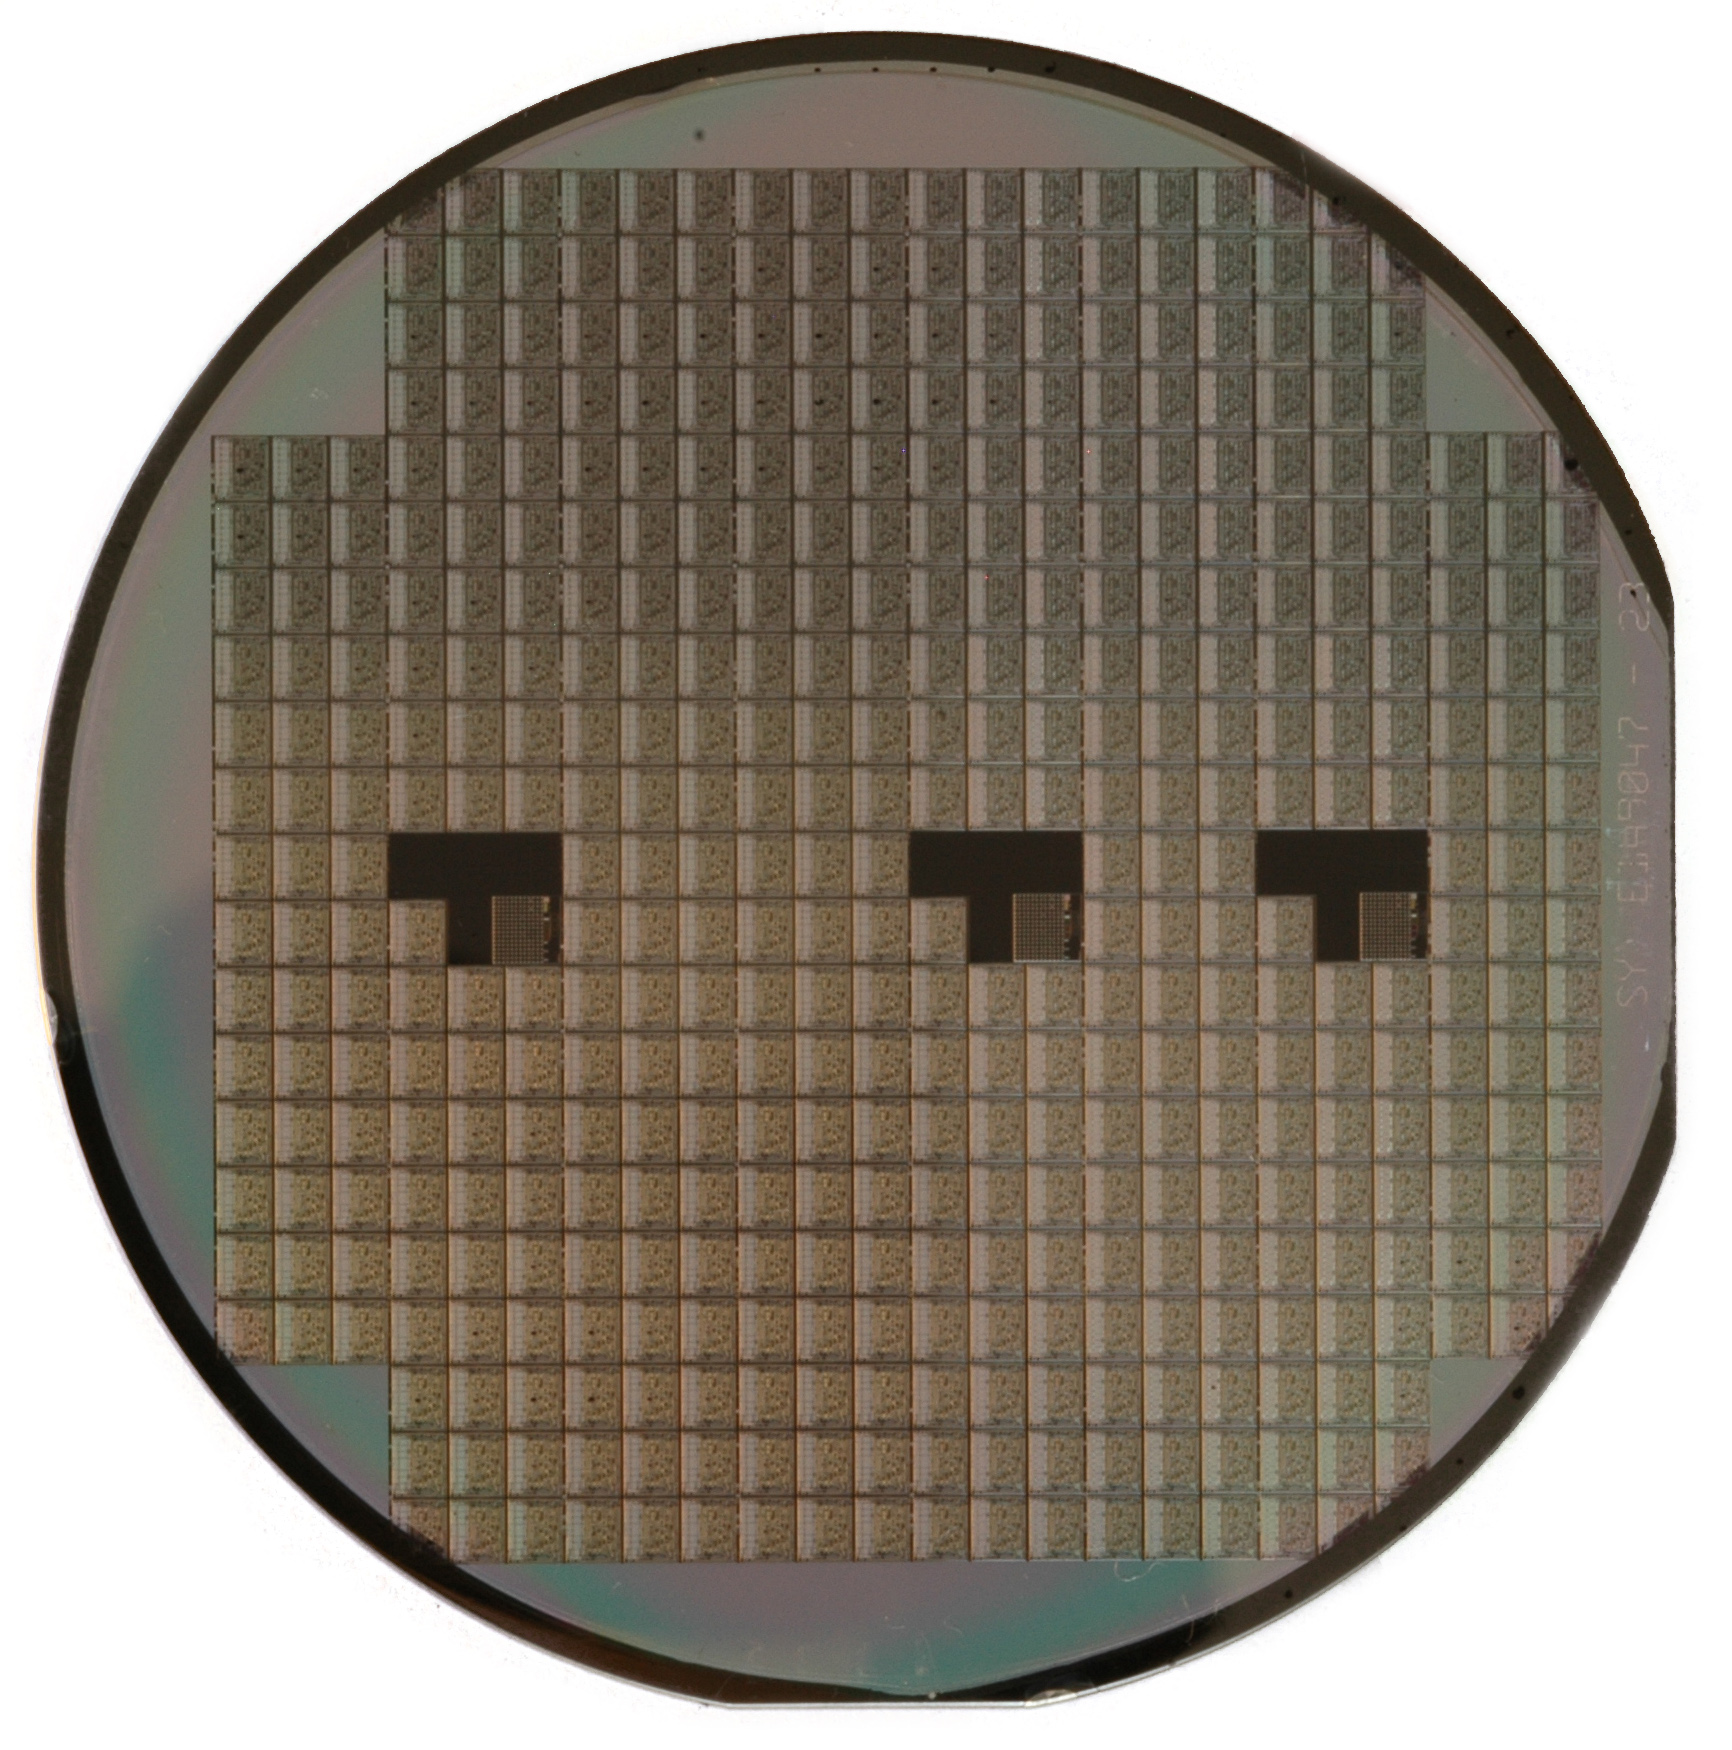
Diamond wafers make package cooling a qualification test
Diamond Foundry reports a 200 mm single crystal. Before teams plan around cooler AI accelerators, they need comparable junction temperatures, interface reliability and production yield.
· 2 min read

BioBasicsBench makes failed controls the test for lab agents
OpenAI's 100-task wet-lab benchmark shows a higher average score alongside wrong colony selections and counting errors. Lab assistants need explicit control checks and human review before their output guides the next experiment.
· 2 min read
All insights
195 articles
AI Security · · 2 min read
An 11-minute agent exploit makes response speed a security control
Amazon says Cairn agents reached arbitrary file write in a medical-imaging app in about 11 minutes. The incident makes containment time part of the threat model, while long failed campaigns show that persistence matters as much as capability.